#904 by installs
NinjaScanner – Virus & Malware scan
A lightweight, fast and powerful virus scanner for WordPress.
- Installs
- 40,000+
- Rating
- 4.0 (36)
- Updated
- 3 months ago
A true Web Application Firewall to protect and secure WordPress.
| Last updated | October 6, 2026Updated in the last 3 months |
|---|---|
| Tested up to | WordPress 7.1.4Covers WordPress 7.1.4, the current release |
| Needs WordPress | 4.9 or newer |
| Needs PHP | 7.1 or newer |
| First published | March 30, 2013 |
| Support, last two months | 3 of 8 threads resolved (38%) |
4.9 / 5 from 220 reviews
| 5 stars | 210 |
|---|---|
| 4 stars | 2 |
| 3 stars | 1 |
| 2 stars | 1 |
| 1 star | 6 |
A true Web Application Firewall
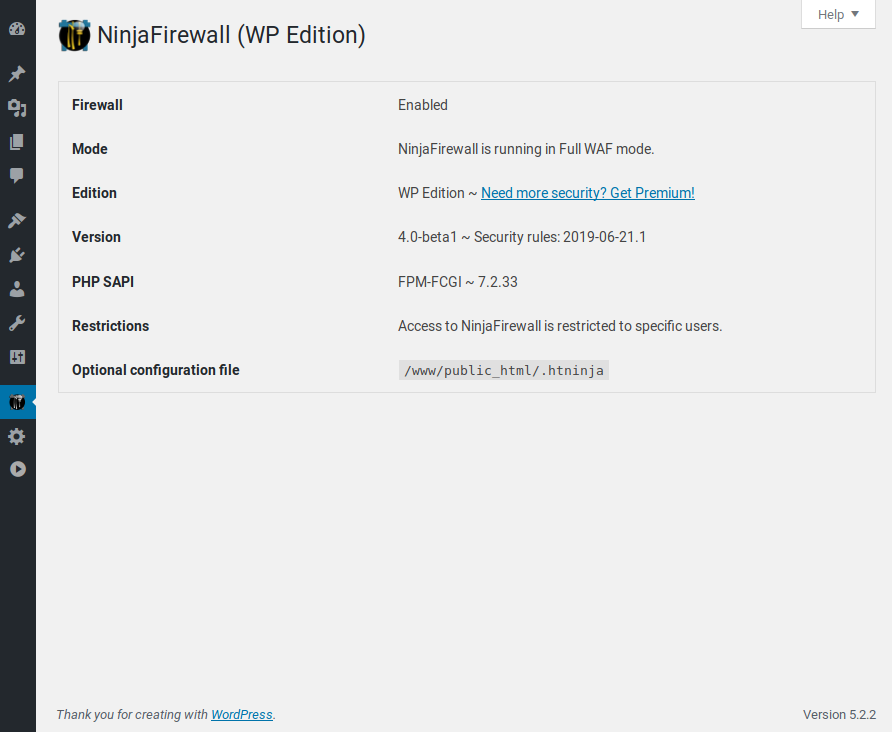
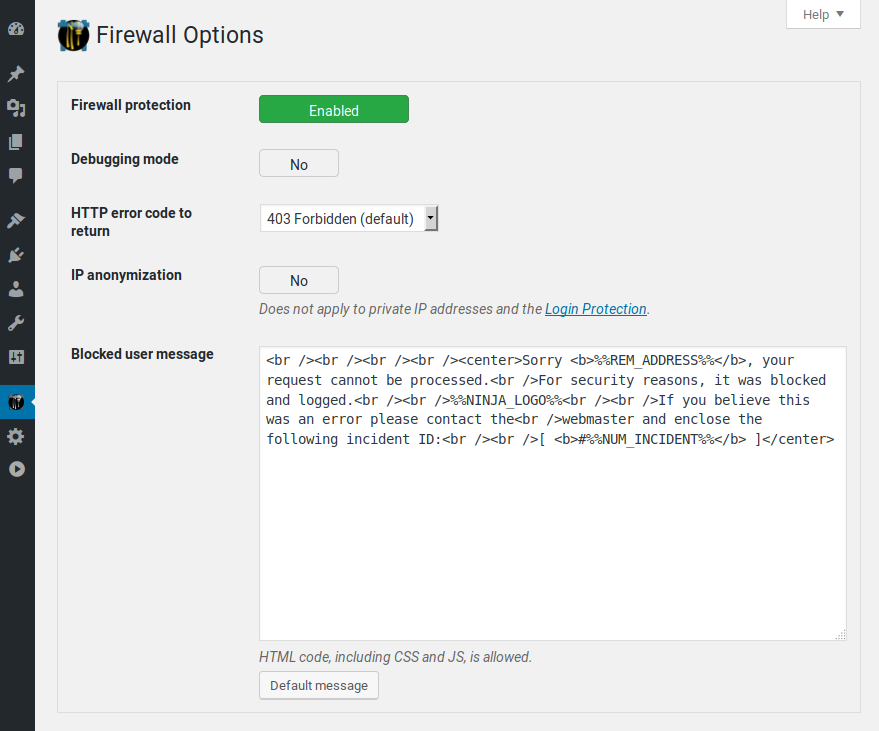
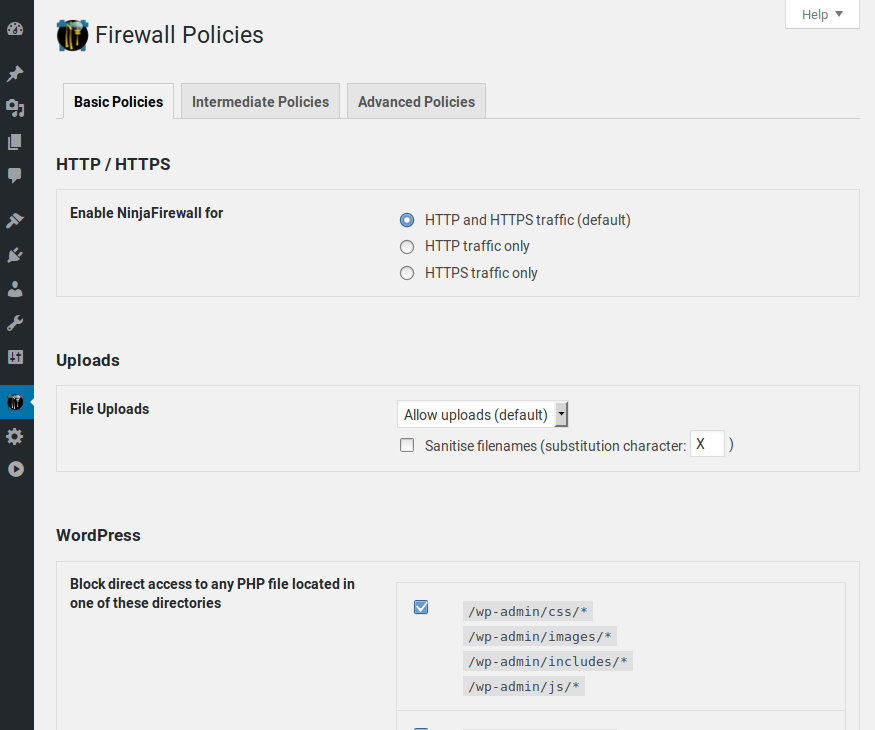
NinjaFirewall (WP Edition) is a true Web Application Firewall. Although it can be installed and configured just like a plugin, it is a stand-alone firewall that stands in front of WordPress.
It allows any blog administrator to benefit from very advanced and powerful security features that usually aren’t available at the WordPress level, but only in security applications such as the Apache ModSecurity module or the PHP Suhosin extension.
NinjaFirewall requires at least PHP 7.1, MySQLi extension and is only compatible with Unix-like OS (Linux, BSD). It is not compatible with Microsoft Windows.
NinjaFirewall can hook, scan, sanitise or reject any HTTP/HTTPS request sent to a PHP script before it reaches WordPress or any of its plugins. All scripts located inside the blog installation directories and sub-directories will be protected, including those that aren’t part of the WordPress package. Even encoded PHP scripts, hackers shell scripts and backdoors will be filtered by NinjaFirewall.
Powerful filtering engine
The opening of the plugin's own description. The full text, installation notes and changelog are on its WordPress.org page.
NinjaFirewall stands between the attacker and WordPress. It can filter requests before they reach your blog and any of its plugins. This is how it works :
Visitor -> HTTP server -> PHP -> NinjaFirewall #1 -> WordPress -> NinjaFirewall #2 -> Plugins & Themes -> WordPress exit -> NinjaFirewall #3
And this is how all WordPress plugins work :
Visitor > HTTP server > PHP > WordPress > Plugins -> WordPress exit
NinjaFirewall includes a very powerful filtering engine which can detect Web Application Firewall evasion techniques and obfuscation tactics used by hackers, as well as support and decode a large set of encodings. See our blog for a full description: An introduction to NinjaFirewall 3.0 filtering engine.
NinjaFirewall does not require any root privilege and is fully compatible with shared hosting accounts. You can install it from your WordPress admin console, just like a regular plugin.
NinjaFirewall works with Nginx and others Unix-based HTTP servers (Apache, LiteSpeed etc). Its installer will detect it.
You do not need to make any modifications to your scripts. NinjaFirewall hooks all requests before they reach your scripts. It will even work with encoded scripts (ionCube, ZendGuard, SourceGuardian etc).
NinjaFirewall will look for the wp-config.php script in the current folder or, if it cannot find it, in the parent folder.
#904 by installs
A lightweight, fast and powerful virus scanner for WordPress.
Firewall, Malware Scanner, Two Factor Auth, and Comprehensive Security Features, powered by our 24-hour team. Make security a priority with Wordfence.
The Sucuri WordPress Security plugin is a security toolset for security integrity monitoring, malware detection and security hardening.
#522 by installs
WordPress security plugin with malware scanner, IP blocking, audit logs, antivirus scans, firewall, 2FA, brute force login security, and more.
#882 by installs
Protect WordPress from malware, hackers, brute-force attacks & suspicious traffic. Includes firewall, login security, 2FA & vulnerability checks.

WordPress login security with brute force protection, Two-factor authentication (2FA/MFA), firewall, IP/country blocking, and login monitoring
Read from the WordPress.org plugin API on , when WordPress 7.1.4 was the current release. WordPress.org rounds active installs into buckets. These are the directory's figures, not my verdict, and I haven't tested this plugin.

